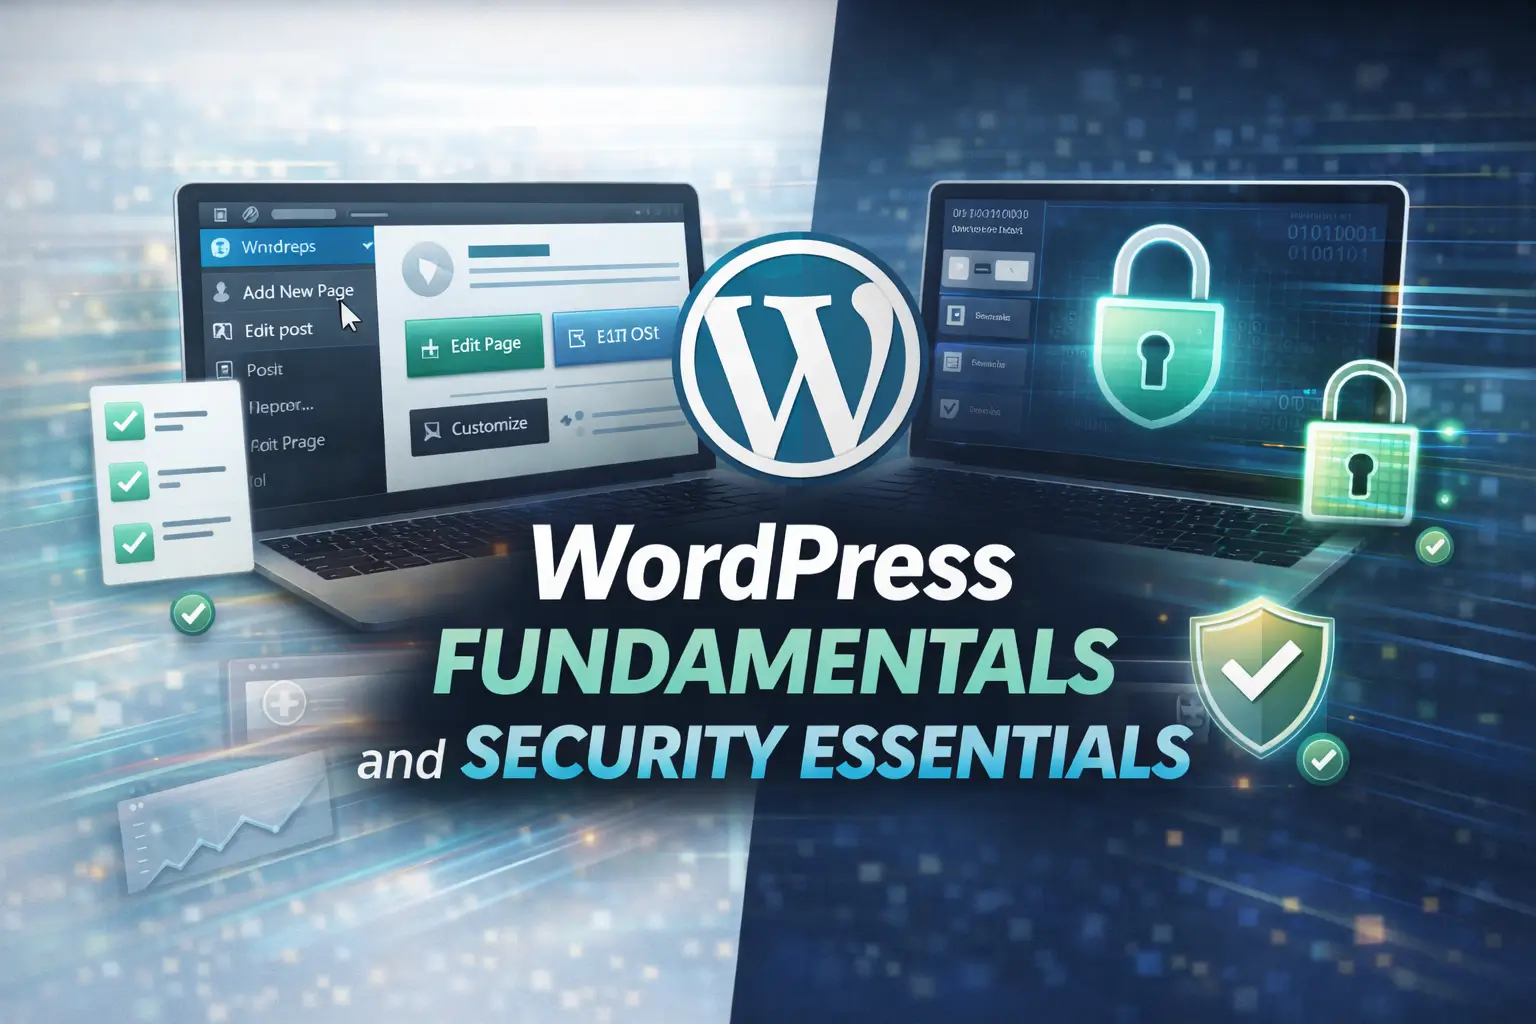
A WordPress site can be a lead generator, sales page, portfolio, client portal, or the home base for your entire business. If it gets compromised, the immediate problem is rarely just technical. You can lose inquiries, search visibility, customer trust, and valuable time. Learning how to protect a WordPress website is therefore not a task to put off until your site is larger. It is a basic business system worth setting up early.
The good news is that most small business sites do not need an enterprise security team. They need a few well-chosen controls, applied consistently. Start with the steps below, document what you change, and give yourself a recovery plan before you need one.
Why WordPress security is a business issue
WordPress itself is widely used and actively maintained, but its popularity also makes it a common target. Most successful attacks do not involve someone breaking into a perfectly maintained site through a dramatic technical trick. They take advantage of old plugins, reused passwords, abandoned themes, weak hosting controls, or backups that were never tested.
For a solo business owner or small team, security should protect continuity. The goal is not to make your website impossible to attack. No system can promise that. The goal is to reduce obvious risk, limit damage if something goes wrong, and restore your site quickly without guessing.
How to protect a WordPress website step by step
1. Keep WordPress, plugins, and themes current
Updates close known security gaps. When you delay updates for months, you increase the chance that an automated bot finds a weakness that already has a public fix.
Check for updates at least weekly, especially if your site uses several plugins. Before making larger updates, create a backup and update one major component at a time. This makes it easier to identify the cause if a page or feature breaks.
There is a trade-off here. Automatically applying every update can be convenient, but a plugin conflict can affect a sales page or checkout without warning. Automatic minor WordPress updates are generally sensible. For plugins, use automatic updates only for tools you trust and monitor. If your site generates regular leads or revenue, schedule a short weekly maintenance check instead of relying on blind automation.
2. Remove anything you do not use
An inactive plugin or theme is not harmless just because it is turned off. If it remains installed, it can still contain an exploitable vulnerability. Delete unused plugins, old themes, demo content, and inactive user accounts.
Keep one current default WordPress theme as a fallback, then remove the rest unless you have a specific reason to retain them. Also avoid installing plugins just to test an idea and forgetting about them later. Every added component creates a maintenance obligation.
Before adding a new plugin, ask three practical questions: Does it solve a real business need? Is it regularly updated? Can your existing theme, host, or another tool already do the job? Fewer moving parts usually means fewer security and performance problems.
3. Strengthen every login path
Weak passwords and reused credentials are still among the fastest ways to lose access to a site. Use a password manager to create a unique, long password for every WordPress administrator account, hosting account, domain registrar account, and business email account.
Enable two-factor authentication for administrator users. This adds a second check, usually through an authenticator app, if a password is stolen. It is one of the highest-value protections you can add because a leaked password alone will not be enough to log in.
Avoid sharing one administrator login across a team. Give each person their own account and only the permissions they need. A writer may need access to posts, for example, but not to plugins, themes, payment settings, or user management. When a contractor finishes a project, remove their account rather than leaving it available for future use.
4. Use secure hosting and protect the server layer
Your web host is part of your security setup. A low-cost plan may be enough for a simple brochure site, but it should still provide current PHP versions, SSL certificates, malware monitoring or scanning options, server-side backups, and responsive support.
Make sure your site uses HTTPS on every page. HTTPS encrypts data moving between visitors and your website, which matters for contact forms, logins, payments, and customer trust. It is not a complete security solution, but it is a required baseline.
Ask your host how it handles suspicious activity, backups, and account isolation. On shared hosting, one poorly secured account should not be able to affect every other account on the server. The answer may influence whether a slightly higher-priced managed plan is worth it for your business.
5. Add a focused security plugin and firewall
A reputable WordPress security plugin can help with firewall rules, malware scans, login protection, file-change alerts, and suspicious activity monitoring. Think of it as an early-warning system and a filter for common attacks, not a replacement for updates and strong passwords.
Set it up carefully. Enable login rate limiting to slow repeated password attempts, turn on alerts for new administrator accounts and changed core files, and review the firewall settings. If you receive dozens of low-priority notifications, adjust them. Security alerts only help when someone can recognize the important ones.
Do not stack multiple security plugins that perform the same job. They can conflict, consume site resources, and create confusion about which tool is actually protecting what. Choose one primary security tool, understand its settings, and review it monthly.
6. Create backups you can actually restore
A backup is only useful if it is recent, complete, stored separately from your hosting account, and capable of being restored. Your backup should include both website files and the database. Posts, form entries, settings, products, and customer data often live in the database rather than in your theme files.
For a site that changes daily, back up daily at minimum. For an ecommerce site, membership site, or active course platform, you may need more frequent database backups. A static portfolio site can usually use a less frequent schedule, but it still needs a backup before updates or design changes.
Keep copies in at least two locations. Host backups are useful, but an off-site copy protects you if your hosting account is inaccessible or a backup fails. Most importantly, test a restoration in a staging site or separate environment. The first time you restore a backup should not be during an outage.
7. Limit access to sensitive areas
Every account, form, and integration is a possible access point. Review WordPress users monthly and check who has administrator privileges. Pay special attention to former freelancers, old staff accounts, and unfamiliar usernames.
If your hosting provider allows it, restrict access to sensitive tools such as the hosting dashboard and database manager. You can also disable direct file editing from inside the WordPress dashboard. That will not stop every attack, but it can reduce the damage if an administrator account is compromised.
Be cautious with API keys and third-party integrations. Marketing platforms, payment processors, scheduling tools, and AI tools can all connect to your site. Store keys securely, remove integrations you no longer use, and rotate credentials when a vendor account or team member changes.
8. Monitor the site and prepare an incident plan
Protection is not a one-time install. Set a recurring calendar reminder to check updates, backups, administrator accounts, security alerts, and core site functions. Test your contact form, checkout, and key landing pages after significant changes. These are small checks that prevent long periods of unnoticed damage.
Write down what you would do if the site were hacked or unavailable. Your plan should identify who can access hosting, domains, backups, and business email; where your most recent backup is stored; and how you will communicate with customers if needed. Keep this information in a secure password manager or internal document, not only inside WordPress.
If you suspect a compromise, avoid making random changes that destroy useful evidence. Put the site into maintenance mode if appropriate, contact your host, change all relevant passwords, scan the site, and restore from a known-clean backup if necessary. Then identify the entry point so the same problem does not return.
A simple maintenance rhythm for small teams
Security becomes manageable when it has a routine. Each week, review updates and make a fresh backup before applying important changes. Each month, review users, delete unused plugins and themes, check security alerts, and confirm that backups are completing. Each quarter, test a restoration and review your hosting and access setup.
This rhythm is more useful than chasing every new security headline. Your business needs systems that get completed, not a complicated checklist that sits untouched in a project folder.
A protected WordPress site gives you more than technical peace of mind. It gives you room to publish, market, collect leads, and improve your business without wondering whether one forgotten plugin could interrupt the work you have built. Set aside an hour this week, start with the highest-risk gaps, and turn website security into a repeatable operating habit.

0 Comments